Guide
After a failed PCI scan: fix, rescan, file
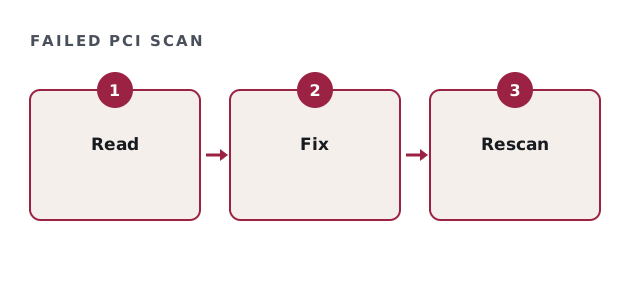
A failed PCI scan is common and usually fixable within the quarter. The steps are simple: read the report, fix or dispute each item, rescan and file the passing result.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
Why a failed PCI scan happens
The approved scanning vendor flags issues above a set severity. For example, outdated software or weak configuration on an internet-facing system. So a failure is a to-do list, not a verdict on the program.
Because the requirement is four passing scans a year, what matters is fixing it within the quarter.
Reading a failed PCI scan report
The report lists each failing item, the system and the reason. Then it shows the severity. Also check for items the vendor marked as needing your input.
| Field | What to do |
|---|---|
| Failing item | Assign an owner |
| Affected system | Confirm it is yours and in scope |
| Severity | Prioritize the highest first |
| Vendor notes | Answer any questions |
| Deadline | Fix and rescan within the quarter |
Failed PCI scan recovery check
Tick what is done.
Your result appears here as you tick, so you can see what is still open.
Fixing or disputing a failed PCI scan
Most items need a patch or a configuration change. However, some may be false positives. In that case, file a dispute with the scanning vendor and attach evidence.
Also tell the vendor about compensating measures. They decide whether to accept them.
Rescanning and filing
Rescan once fixes are done. Then file both the failing and the passing reports. As a result, the QSA sees the full story for that quarter.
In addition, note what caused the failure, so it does not repeat.
Preventing the next failed PCI scan
Run your own checks before the official scan. Also tie patching to a regular schedule. Because most failures repeat, the same systems usually need attention.
So add those systems to the monthly review.
Where Ashcroft helps
We help you read the report, organize fixes with your teams or partners and prepare the evidence. Our gap analysis fee runs $8,000 to $40,000. We are not a QSA or a scanning vendor. Approved vendors appear on the official Approved Scanning Vendor list.
Failed PCI scan questions
Is a failed PCI scan a compliance failure?
Not if you fix it and get a passing rescan within the quarter.
How fast should a failed PCI scan be fixed?
Within the quarter, so you still have a passing scan for it.
Can we dispute a failed PCI scan?
Yes, with evidence, through the scanning vendor.
Do we keep the failing report?
Yes. File it next to the passing rescan.
Related guides
Recover from a failed PCI scan
Send us the scan summary. We reply with a written estimate, usually inside one business day.
Get my written estimate