Guide
The PCI DSS 12 requirements, explained without jargon
The PCI DSS 12 requirements are the rules any business handling card data must follow. They were written by the card brands, and every assessment works through them one by one.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
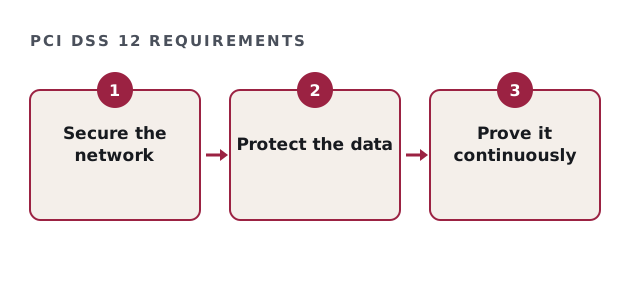
The PCI DSS 12 requirements at a glance
The requirements group into six goals. So it helps to read them in that order. The full standard is in the PCI SSC document library.
| # | Requirement in plain words |
|---|---|
| 1 | Install and maintain network security controls. |
| 2 | Apply secure configurations to all systems. |
| 3 | Protect stored account data. |
| 4 | Encrypt card data sent over public networks. |
| 5 | Protect systems from malicious software. |
| 6 | Develop and maintain secure systems and software. |
| 7 | Restrict access to what each role needs. |
| 8 | Identify users and authenticate access. |
| 9 | Restrict physical access to card data. |
| 10 | Log and monitor all access. |
| 11 | Test security regularly. |
| 12 | Support security with policies and programmes. |
Where businesses usually fail the PCI DSS 12 requirements
Most failures cluster in a few places. For example, requirement 10 needs logs that someone reviews, while requirement 11 needs regular scans and tests. Also, requirement 12 needs written policies that people follow. Therefore those three deserve early attention.
PCI DSS 12 requirements quick check
Tick what you could evidence today. Gaps show where to start.
Your result appears here as you tick, so you can see what is still open.
What changed in version 4.0.1
Version 4.0.1 added new requirements that became mandatory on 31 March 2025. For example, 6.4.3 covers every script on your payment page, 11.6.1 covers tamper detection on that page, and 8.4.2 extends multi-factor authentication to all access into the card environment.
Not every requirement applies to everyone
Which requirements apply depends on how you take payments. So a business using a fully hosted checkout may answer only a small subset on a short questionnaire. However, a business storing card data faces almost all of them.
That is why scoping comes first. A smaller card environment means fewer systems to protect, fewer requirements to evidence and a lower cost overall.
Our role with the PCI DSS 12 requirements
We prepare businesses against the requirements: gap analysis, remediation, policies and evidence. However, we are not a QSA, so we never perform the assessment. When you need one, we introduce an independent QSA.
PCI DSS 12 requirements questions
Do all the PCI DSS 12 requirements apply to small merchants?
Not always. Your questionnaire type decides which apply, so a hosted checkout reduces them sharply.
Who wrote the requirements?
The card brands, through the PCI Security Standards Council.
How often are the PCI DSS 12 requirements updated?
Major versions arrive every few years. Version 4.0.1 is current.
Is PCI DSS a law?
No. It is a contractual requirement from the card brands, passed on through your bank.
Related guides
Get ready for the PCI DSS 12 requirements
Tell us how you take payments. We reply with a written estimate for readiness, and we introduce a QSA when you need one.
Get my written estimate