Guide
The PCI ROC: the full Report on Compliance, and who needs one
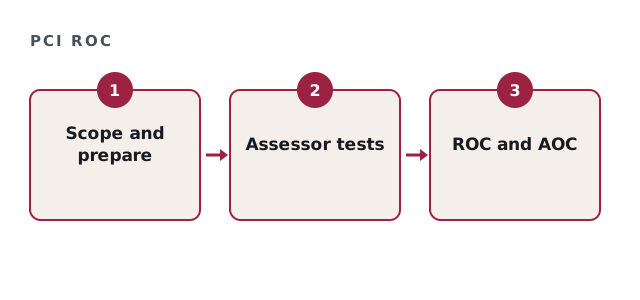
A PCI ROC, or Report on Compliance, is the full assessment report, often hundreds of pages long. Large merchants and many service providers need one, and only a qualified assessor can produce it.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
Who needs a PCI ROC
Level 1 merchants and Level 1 service providers usually need one. Also, an acquirer can require a ROC from any business it considers high risk. Templates are in the PCI SSC document library.
Who may sign it
The rules on signing are strict.
| Business type | Who may sign the ROC |
|---|---|
| Merchant | A QSA, or a qualified internal assessor. |
| Service provider | A QSA only. |
PCI ROC readiness check
Tick what is in place before the assessor starts.
Your result appears here as you tick, so you can see what is still open.
What a PCI ROC costs
A QSA-led ROC assessment typically runs $50,000 to $250,000 in the US market. However, readiness and remediation are usually the larger part of the total. Also, a full report quoted under $35,000 usually means the scope is unrealistic.
Preparing for the assessor
Most businesses struggle because evidence is scattered. Therefore collect it before the assessor arrives, organised by requirement.
- Scope documented and agreed
- Network and data flow diagrams current
- Evidence filed by requirement
- Owners ready for interviews
An organised evidence set shortens fieldwork, so the assessor spends time testing rather than waiting.
Our role with the PCI ROC
We prepare the environment and the evidence, then coordinate with your QSA. However, we never perform the assessment or sign a ROC, because we are not a QSA. You can check firms on the official QSA company list.
Also agree a single point of contact for the assessor, so questions do not bounce between teams. In addition, keep a log of requests and responses. That log shows progress and prevents duplicate work later. Finally, plan remediation time after fieldwork, because findings often need fixing before the report can close. Budget for that remediation window from the very start.
PCI ROC questions
How long does a PCI ROC take?
It depends on scope, but preparation usually takes longer than the assessment itself.
Can we self-assess instead?
Only if your level and acquirer allow a questionnaire.
Who keeps the PCI ROC?
You and your assessor, while banks usually receive the AOC.
Do you sign ROCs?
No. We are not a QSA.
Related guides
Prepare for your ROC assessment
Tell us your level and scope. We reply with a written readiness estimate and can introduce QSA firms.
Get my written estimate