Guide
The PCI targeted risk analysis, in plain terms
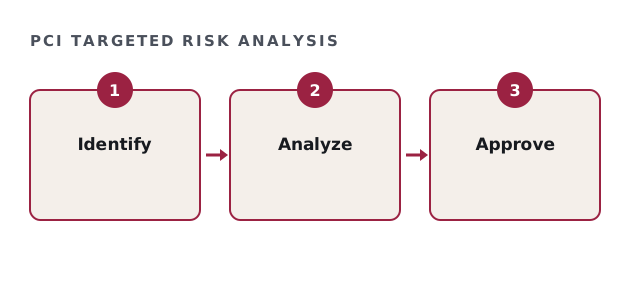
A PCI targeted risk analysis justifies how often certain controls run. Requirement 12.3.1 asks for one wherever the standard lets you choose the frequency, so each choice needs a short written reason.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
What a PCI targeted risk analysis is
Some requirements let you set the frequency. For example, how often a review happens. Then 12.3.1 asks you to document why your chosen frequency fits the risk.
So it is a short, focused document for each flexible control, rather than one big risk assessment.
What to include
Keep each analysis to a page. The table shows the usual fields.
| Field | Content |
|---|---|
| Requirement | Which control it covers |
| Asset and threat | What is protected and from what |
| Factors | What makes the risk higher or lower |
| Frequency | The chosen interval and why |
| Approval | Who approved it and when |
| Review | When it will be revisited |
PCI targeted risk analysis check
Tick what exists.
Your result appears here as you tick, so you can see what is still open.
Writing a PCI targeted risk analysis
Describe the asset, the threat and the factors that affect likelihood. Then state the frequency and explain the reasoning. Also keep the language plain.
Because the QSA reads the reason, a copied template with no local detail will raise questions.
Approving and reviewing it
Leadership or the security lead approves each one. Then review them at least once a year. In addition, update them when the environment changes.
As a result, the frequencies stay matched to real risk.
How it fits with the wider risk assessment
Your general risk assessment covers the whole program. Meanwhile, targeted analyses cover single controls. So link them, and keep owners consistent.
Then the QSA sees one coherent approach.
Where Ashcroft helps
We list the controls that need an analysis, draft each one and set up review records. Policy and documentation work runs $10,000 to $30,000. We are not a QSA. The standard is in the PCI SSC document library.
Also keep the analyses in one place. Because the QSA asks for them together, a single folder saves time. So name each file by requirement number. In addition, note the next review date inside each one.
PCI targeted risk analysis questions
Which controls need a PCI targeted risk analysis?
Those where the standard lets you choose the frequency.
How long is a PCI targeted risk analysis?
Usually a page per control.
Who approves a PCI targeted risk analysis?
Leadership or the security lead, with a date.
Is it the same as the annual risk assessment?
No. It covers one control, not the whole program.
Related guides
Write each PCI targeted risk analysis
Tell us your scope and current policies. We reply with a written estimate, usually inside one business day.
Get my written estimate