Guide
The PCI ASV scan: quarterly, external and only from approved vendors
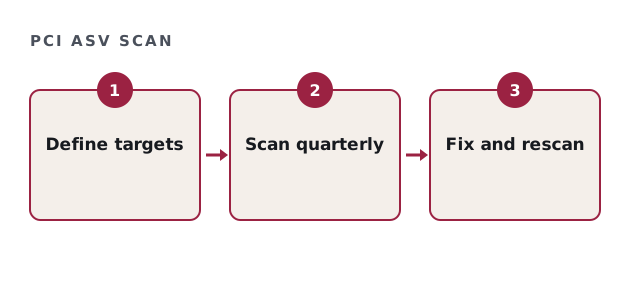
A PCI ASV scan is a quarterly external vulnerability scan run by an Approved Scanning Vendor. So it checks everything of yours facing the internet that could affect card data, and only a listed vendor may run it.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
Who may run a PCI ASV scan
Only companies on the official Approved Scanning Vendor list may produce the scan report your bank accepts. Therefore an ordinary scanning tool, however good, does not satisfy the requirement on its own.
How often it is due
External scans are required at least once every three months, and after significant changes. Also, each quarter needs a passing result, so a failed scan must be fixed and rescanned.
| Item | Typical rule |
|---|---|
| Frequency | At least quarterly. |
| After changes | Rescan after significant changes. |
| Passing | No vulnerabilities above the allowed threshold. |
| Market price | About $1,200 to $8,000 a year. |
PCI ASV scan readiness check
Tick what is in place.
Your result appears here as you tick, so you can see what is still open.
What causes a failed PCI ASV scan
Failures usually come from outdated software, weak encryption settings or services exposed by mistake. So fixing them is often straightforward, but it takes time.
- Outdated web server or framework versions
- Weak TLS settings
- Exposed admin interfaces
- Forgotten hosts left online
Disputes and false positives
Sometimes a scan flags something that is not really exploitable. In that case, you can dispute it with evidence through the vendor. However, document the reasoning carefully, because the vendor decides.
Our role with the PCI ASV scan
We do not run ASV scans, because that requires an approved vendor. Instead, we help you define targets, fix failures and prepare dispute evidence. We are not a QSA either.
Plan the first quarter carefully, because it often finds the most issues. Then later quarters usually pass quickly, as long as nobody adds a new service without telling the person who manages the scan scope.
PCI ASV scan questions
Can we run the PCI ASV scan ourselves?
No. Only a listed Approved Scanning Vendor can produce an accepted report.
Is an ASV scan a penetration test?
No. It is an automated scan, while penetration testing is a separate requirement.
What happens if a PCI ASV scan fails?
You fix the issues and rescan until it passes for that quarter.
Do you run scans?
No. We help you prepare and fix, while an approved vendor scans.
Related guides
Get your scans passing every quarter
Tell us your internet-facing systems. We reply with a written estimate for remediation support.
Get my written estimate