Guide
PCI audit log requirements: what to log, review and keep
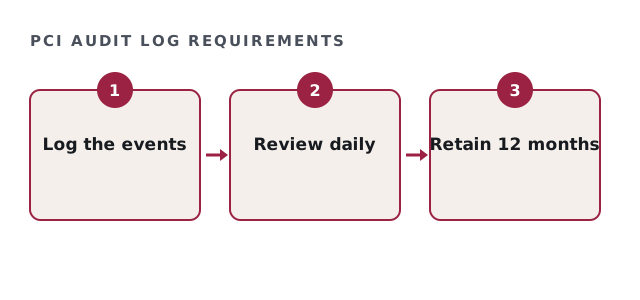
PCI audit log requirements come from Requirement 10. They ask you to log access to card data, review the logs regularly and keep them for a set period. So logging without review does not pass.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
What PCI audit log requirements say to log
Requirement 10 lists specific events. Therefore configure logging to capture each one. The text is in the PCI SSC document library.
- All individual access to cardholder data
- All actions by administrative accounts
- Access to the audit logs themselves
- Invalid access attempts
- Changes to accounts and authentication
- Starting, stopping or pausing logs
Retention and review in PCI audit log requirements
The retention rule has two parts, and both matter.
| Rule | What it asks |
|---|---|
| Retention | At least 12 months of audit log history. |
| Immediate access | The most recent three months available at once. |
| Review | Security events reviewed at least daily. |
| Automation | Automated review mechanisms are expected. |
PCI audit log requirements check
Tick what is in place.
Your result appears here as you tick, so you can see what is still open.
Meeting PCI audit log requirements without drowning
Daily review sounds heavy. However, version 4.0.1 expects automated mechanisms, so tools filter events and people review the alerts. Also, keep a record of each review, because the assessor will ask for it.
Time sync and protection under PCI audit log requirements
Clocks must be synchronised, so events line up across systems. Also, logs must be protected from change, because an attacker's first step is often to erase them.
In practice that means a central log store with restricted write access, plus alerts when logging stops.
Our role
We design logging and review processes that fit your environment. However, we are not a QSA, so validation remains with you or your assessor.
Start with the systems inside the card environment, then extend to the systems connected to it. As a result, the highest-risk logs are covered first, while the rest follow in a planned order rather than all at once.
PCI audit log requirements questions
How long must logs be kept under PCI audit log requirements?
At least 12 months, with the last three months immediately available.
Do we need a SIEM?
Not strictly, but automated review is expected, so a tool usually helps.
Do PCI audit log requirements mean a person reads logs daily?
Automated mechanisms review them, while people act on alerts and keep records.
Are logs themselves protected?
Yes. Access to logs must be restricted and logged.
Related guides
Design logging that passes and scales
Tell us your environment. We reply with a written estimate for logging design and review processes.
Get my written estimate