Guide
The PCI internal vulnerability scan, quarter by quarter
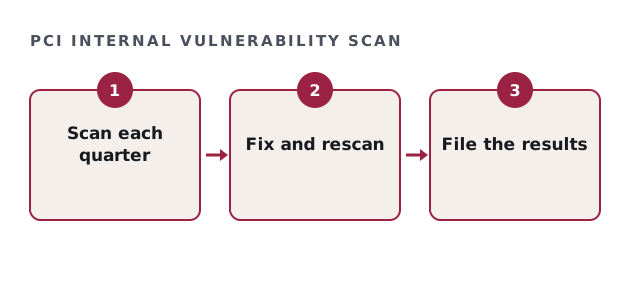
A PCI internal vulnerability scan looks at systems inside your network every three months. Unlike the external scan, it does not need an Approved Scanning Vendor, but it does need discipline.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
What a PCI internal vulnerability scan is
It is an automated scan of in-scope internal systems. So it finds known weaknesses before an attacker inside the network does. Also, it complements the external scan, which an ASV must perform.
PCI internal vulnerability scan rules
Version 4.0 of the standard sets a clear rhythm. However, the detail is where merchants slip.
| Rule | What it means |
|---|---|
| Frequency | At least once every three months, and after significant changes. |
| Resolution | High-risk and critical findings fixed, then rescanned to confirm. |
| Authentication | Scans use credentials, so they see more than an outside view. |
| Who runs it | Qualified staff or a third party, with independence from the systems. |
PCI internal vulnerability scan check
Tick what is true for the last four quarters.
Your result appears here as you tick, so you can see what is still open.
Common PCI internal vulnerability scan gaps
A missed quarter is the most common gap. For example, a scan fails in March and nobody reruns it before April.
- A quarter with no clean result
- Systems missing from the scan scope
- Findings closed without a rescan
- Scanner credentials that no longer work
Internal compared with external scanning
External scans face the internet and need an ASV. Internal scans face your own network and can run in-house. Therefore you need both, and each has its own evidence trail.
Where we help
We are not an ASV or a QSA. However, we set up the scan rhythm, review results and close gaps before your assessment. Approved scanning vendors are listed on the official Approved Scanning Vendor list for the external side.
PCI internal vulnerability scan questions
Does a PCI internal vulnerability scan need an ASV?
No. An ASV is required only for external scans.
What if we miss a PCI internal vulnerability scan?
Run it as soon as possible and record why. A QSA will ask about any gap.
Is a PCI internal vulnerability scan the same as a penetration test?
No. A scan is automated, while a penetration test is manual and deeper.
Which findings must be fixed?
High-risk and critical ones, with a rescan to prove it.
Related guides
Set up your PCI internal vulnerability scan rhythm
Send five answers about your environment and receive a written estimate, usually inside one business day.
Get my written estimate