Guide
PCI segmentation testing, and the evidence your QSA will ask for
PCI segmentation testing proves that the networks you call out of scope really cannot reach the cardholder data environment. So it protects the scope reduction that keeps your assessment smaller.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
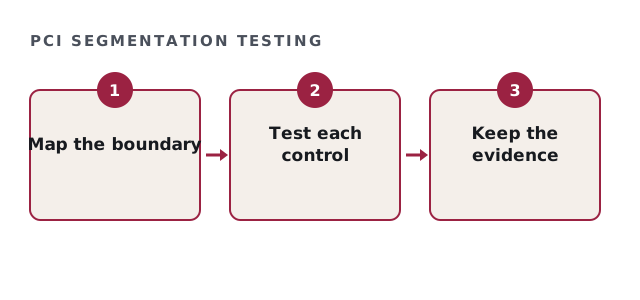
Why PCI segmentation testing exists
Segmentation is optional under PCI DSS. However, if you rely on it to shrink scope, you must prove it works. Otherwise every connected system falls back into scope, and the assessment grows.
Therefore the test is not a formality. It is the evidence behind the boundary you drew.
How often PCI segmentation testing runs
The frequency depends on who you are. Also, any change to the segmentation controls triggers a new test.
| Entity | Minimum frequency |
|---|---|
| Merchant | At least once every 12 months, and after changes to segmentation controls. |
| Service provider | At least once every six months, and after changes. |
PCI segmentation testing readiness check
Tick what is already true. Each open item is a likely QSA question.
Your result appears here as you tick, so you can see what is still open.
What PCI segmentation testing covers
The test checks each method you use to isolate the cardholder data environment. For example, firewall rules, VLAN controls and cloud security groups.
- Every segmentation control in use, not a sample
- Paths from each out-of-scope network towards the cardholder data environment
- Confirmation that isolation actually holds
- Written results the QSA can review
Who can perform the test
PCI DSS asks for a qualified tester with organisational independence. So it can be internal staff, but not the people who manage those controls. Many merchants use an outside firm for that reason.
Where we help
We are not a QSA, so we do not assess. However, we map the boundary, check the rules and organise the evidence before testing starts. Readiness work sits in our $8,000 to $40,000 gap analysis range. The requirement text is in the PCI SSC document library.
PCI segmentation testing questions
Is PCI segmentation testing mandatory?
Only if you use segmentation to reduce scope. Without segmentation, the whole network is in scope instead.
Can a vulnerability scan replace PCI segmentation testing?
No. A scan lists known issues, while segmentation testing checks whether isolation actually holds.
Does PCI segmentation testing count as a penetration test?
It is part of the penetration testing requirement. So it is often done in the same engagement.
What if the test finds a path into the cardholder data environment?
Fix the control, then retest. Until then, the connected systems are treated as in scope.
Related guides
Prepare for PCI segmentation testing
Send five answers about your environment. We reply with a written estimate, usually inside one business day, and nothing starts until you agree.
Get my written estimate