Guide
PCI DSS 6.4.3 and the payment page script inventory
PCI DSS 6.4.3 covers every script that loads on your payment page. Each one needs authorization, a written reason and a place in an inventory, so the work is mostly a governance task.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
What PCI DSS 6.4.3 asks for
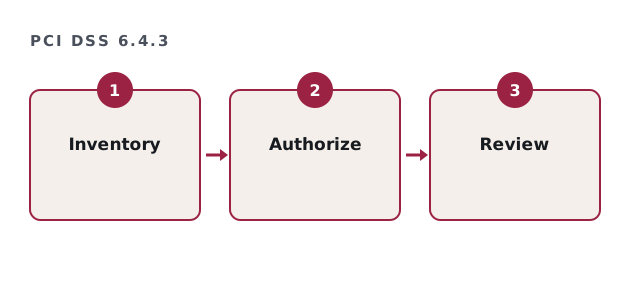
The requirement has three parts. Scripts must be authorized, their integrity must be assured, and an inventory must list each one with a written justification.
So the evidence is a list, an approval trail and a description of how integrity is checked. Because marketing and engineering both add scripts, both teams take part.
| Part | Evidence |
|---|---|
| Authorization | Approval record per script |
| Justification | Written business reason |
| Inventory | Current list with owners |
| Integrity | Description of the method used |
| Review | Dated periodic reviews |
Building the PCI DSS 6.4.3 inventory
List every script on the payment page, including third-party ones. Then name an owner and a reason for each. Also remove scripts nobody can justify.
As a result, the inventory usually gets shorter, which makes ongoing review easier.
PCI DSS 6.4.3 check
Tick what is already in place.
Your result appears here as you tick, so you can see what is still open.
Approval workflow
Set a simple rule: no new script on the payment page without an approved ticket. Then the inventory updates with each approval. In addition, include the person who requested it.
So the trail shows the control working across the year.
How PCI DSS 6.4.3 links to 11.6.1
Requirement 11.6.1 covers detecting unauthorized changes to the same page. So the two are often handled together. Then one inventory serves both.
Also confirm which party owns the page when a provider hosts it, because that changes your duties.
Who owns it
Usually the web or engineering lead owns the inventory. However, marketing must follow the approval rule. So brief both teams.
In addition, review the inventory on the schedule your targeted risk analysis sets.
Where Ashcroft helps
We set up the inventory, the approval rule and the review record. Our gap analysis fee runs $8,000 to $40,000. We are not a QSA. The requirement text is in the PCI SSC document library.
PCI DSS 6.4.3 questions
Does PCI DSS 6.4.3 apply if a provider hosts the payment page?
It depends on how the page is embedded. Check with your provider and QSA.
Who maintains the PCI DSS 6.4.3 inventory?
Usually the web or engineering lead.
Is PCI DSS 6.4.3 mandatory now?
Yes. It became mandatory on March 31, 2025.
Do analytics scripts count?
Yes, if they load on the payment page.
Related guides
Meet PCI DSS 6.4.3 with clear records
Tell us how your payment page is built. We reply with a written estimate, usually inside one business day.
Get my written estimate