Guide
PCI DSS incident response: a plan you have actually tested
PCI DSS incident response is covered by Requirement 12.10. It asks for a written plan, people ready to act at any hour and an annual test. So a document in a drawer is not enough.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
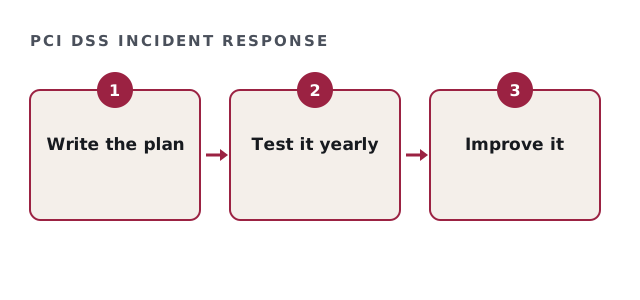
What PCI DSS incident response requires under 12.10
The requirement has several parts. Therefore check each one separately. The text is in the PCI SSC document library.
| Part | What it asks |
|---|---|
| 12.10.1 | A written incident response plan. |
| 12.10.2 | Review and test the plan at least every 12 months. |
| 12.10.3 | Personnel available to respond around the clock. |
| 12.10.4 | Training for those personnel. |
| 12.10.5 | Monitoring alerts included in the plan. |
| 12.10.7 | Procedures for card numbers found where not expected. |
What a PCI DSS incident response plan should cover
A useful plan is short and specific. So it names people, steps and contacts, rather than general principles.
- Roles, with deputies
- How to contain a suspected compromise
- Who to notify, including your acquirer and the card brands
- How to preserve evidence for forensics
- How to restore normal operations
PCI DSS incident response check
Tick what is in place.
Your result appears here as you tick, so you can see what is still open.
Testing PCI DSS incident response
A tabletop exercise is the usual test. For example, walk through a suspected payment page skimmer, from first alert to acquirer notification. Then record what went well and what needs changing, because that record is your evidence.
PCI DSS incident response for unexpected card data
Version 4.0.1 added 12.10.7, which asks for procedures when card numbers are found outside the card environment. Therefore your plan needs a path for that discovery, including how to remove the data and find the cause.
Our role
We help write, test and improve the plan. However, we are not a QSA, so validation remains with you or your assessor.
Keep the plan short enough to use under pressure. A few pages with names, numbers and steps beat a long document nobody can find during an incident.
PCI DSS incident response questions
How often must the PCI DSS incident response plan be tested?
At least once every 12 months.
Does a tabletop exercise count as PCI DSS incident response testing?
Yes, when it is documented with lessons and changes.
Who must we notify after a suspected breach?
Your plan should name your acquirer and follow card brand rules.
Is a general IT incident plan enough?
Only if it covers the card-specific steps the requirement lists.
Related guides
Write and test your plan before you need it
Tell us your current plan, if any. We reply with a written estimate for drafting and a tabletop test.
Get my written estimate