Guide
PCI DSS scoping: what sets the size of your assessment
PCI DSS scoping decides which systems, people and processes the assessment covers. Because every requirement applies to everything in scope, scope is the biggest driver of effort and fees.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
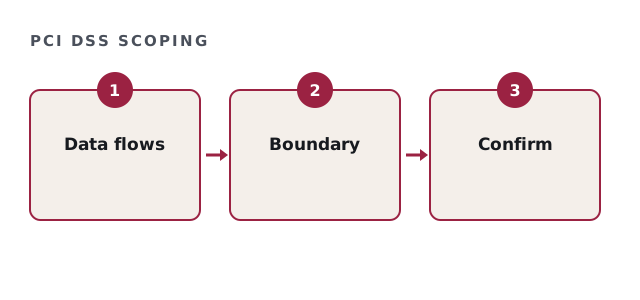
What PCI DSS scoping includes
Scope starts with the cardholder data environment. That means systems that store, process or transmit card data. Then it adds systems that connect to them or can affect their security.
So scope is wider than the payment system alone. For example, an admin workstation that manages the payment server is usually in scope.
What pulls systems into PCI DSS scoping
Most scope surprises come from a few common paths. The table lists them.
| Situation | Effect on scope |
|---|---|
| Card data stored in a system | System in scope |
| System connects to the payment environment | Usually in scope |
| Shared admin accounts or tools | Pulls connected systems in |
| Flat network without segmentation | Large parts of the network in scope |
| Card numbers in email or tickets | Those tools in scope |
PCI DSS scoping check
Tick what you already know.
Your result appears here as you tick, so you can see what is still open.
How segmentation changes PCI DSS scoping
Segmentation isolates the payment environment from the rest of the network. Then fewer systems fall in scope. However, segmentation itself must be tested, every 12 months for merchants and every six months for service providers.
Also outsourcing payment pages or using validated point-to-point encryption can shrink scope sharply. So review the payment flow before anything else.
Why scope drives the fee
More systems mean more interviews, more evidence and more sampling. Because of that, quotes from a QSA or a consultant follow scope closely.
So reducing scope first often saves more than negotiating any price.
Confirming PCI DSS scoping each year
Scope changes as systems change. So confirm it at least once a year and after significant changes. Then document how you reached the boundary.
In addition, keep the data flow diagram and inventory in step with the scope decision.
Where Ashcroft helps
We map card flows, test the scope logic with you and document the boundary for your QSA to review. Our gap analysis fee runs $8,000 to $40,000. We are not a QSA. The standard is in the PCI SSC document library.
PCI DSS scoping questions
Who decides PCI DSS scoping?
The entity defines it. The QSA validates it during the assessment.
Can PCI DSS scoping be reduced?
Yes, through segmentation, outsourcing and removing stored card data.
How often should PCI DSS scoping be reviewed?
At least yearly and after significant changes.
Is a phone line in scope?
It can be, if card numbers pass through it. Check the payment flow.
Related guides
Get PCI DSS scoping right first
Tell us your payment channels and hosting. We reply with a written estimate, usually inside one business day.
Get my written estimate