Guide
Writing the PCI information security policy
The PCI information security policy sits under requirement 12 and ties the program together. It states intent, roles and review cycles, so the QSA reads it first and tests against it.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
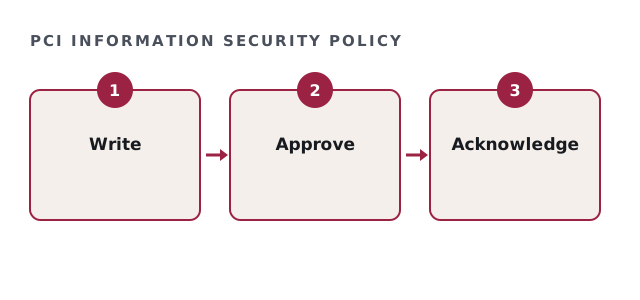
What the PCI information security policy covers
It sets the overall approach to protecting card data. Then it points to topic policies, such as access, logging and incident response. Also it names who is responsible.
Because every requirement links back to it, the policy must match how you actually work.
| Section | Content |
|---|---|
| Purpose and scope | What and who it covers |
| Roles | Security responsibilities by role |
| Topic policies | Links to each supporting policy |
| Risk | How targeted risk analyses are done |
| Awareness | Training under 12.6 |
| Review | Annual review and approval |
Approving the PCI information security policy
Leadership approves it, with a date. Then review it at least once a year and after significant changes. Also keep each approved version.
In addition, record who reviewed it, so the QSA sees the cycle.
PCI information security policy check
Tick what is in place.
Your result appears here as you tick, so you can see what is still open.
Staff acknowledgment
People must know the policy applies to them. So collect acknowledgment at hiring and after major updates. Then link it with security awareness training.
As a result, interviews confirm what the policy says.
Keeping the PCI information security policy practical
Long policies tend to drift from reality. So keep the main policy short and put detail in procedures. Then updates touch only the part that changed.
Also avoid copying templates without editing. The QSA tests what the text says.
Linking to the rest of requirement 12
Requirement 12 also covers risk analysis, awareness, personnel screening, providers and incident response. So the policy should point to each. Because the QSA reads them together, consistency matters.
Then check that dates and owners agree across documents.
Where Ashcroft helps
We write the policy set with your teams and set up review and acknowledgment records. Policy and documentation work runs $10,000 to $30,000. We are not a QSA. The standard is in the PCI SSC document library.
PCI information security policy questions
How often should the PCI information security policy be reviewed?
At least once a year and after significant changes.
Who approves the PCI information security policy?
Leadership, with a recorded date.
Can we use a template for the PCI information security policy?
As a start, but edit it to match how you work.
Do contractors acknowledge it?
If they are in scope, yes.
Related guides
Update your PCI information security policy
Send us your current policy set. We reply with a written estimate, usually inside one business day.
Get my written estimate