Guide
The PCI internal audit, before the real assessment
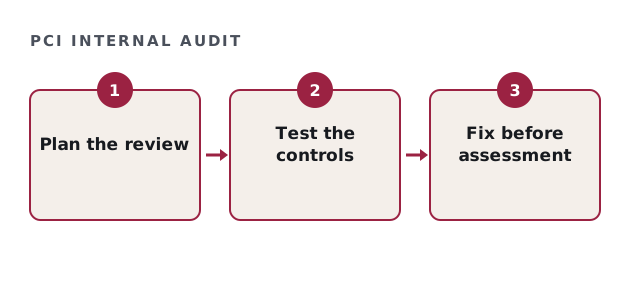
A PCI internal audit tests your controls before an assessor does. So problems surface while there is still time to fix them, rather than in the final report.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
What a PCI internal audit is
It is an internal review of PCI DSS controls against the standard. However, it does not replace validation by a QSA or a self-assessment questionnaire.
Who runs a PCI internal audit
Independence matters, even internally. Therefore the reviewer should not test controls they operate.
| Option | Note |
|---|---|
| Internal audit team | Independent of operations, so findings carry weight. |
| Internal Security Assessor | Staff trained by PCI SSC, accepted by some card brands for certain validation. |
| Outside readiness consultant | Fresh eyes and experience of what QSAs sample. |
PCI internal audit readiness check
Tick what you have already done this year.
Your result appears here as you tick, so you can see what is still open.
What a PCI internal audit should test
Focus where findings usually appear. For example, access reviews, logging, scanning and change records.
- Quarterly scan evidence
- Access reviews and leaver removals
- Log review records
- Policy approval dates
- Third-party provider monitoring
Turning the review into evidence
Record what you tested, what you found and how you fixed it. Also keep dates, because QSAs check that controls operated over time.
Where we help
We run readiness reviews that mirror a QSA's approach. Gap analysis runs $8,000 to $40,000. We are not a QSA, so we prepare and you validate. The standard is in the PCI SSC document library.
Also share the results with management. Because PCI DSS expects leadership to own security, a short summary of findings and fixes builds that record. So the review supports governance as well as readiness. In addition, repeat it each year, because controls drift between assessments.
PCI internal audit questions
Is a PCI internal audit required?
Not as a named requirement. However, it is the best way to avoid surprises.
Can a PCI internal audit replace a QSA?
No. Validation still follows your card brand and acquirer rules.
When should a PCI internal audit happen?
Several months before assessment, so fixes can run long enough to show evidence.
What is an ISA?
An Internal Security Assessor, a staff member trained by PCI SSC.
Related guides
Prepare with a PCI internal audit
Send five answers about your environment. We reply with a written estimate, usually inside one business day. Also tell us your assessment date, because timing decides how much evidence can build up. So the review starts at the right moment, rather than too late to help.
Get my written estimate