Guide
PCI PA DSS is retired: what replaced it and what to do
PCI PA DSS once validated payment applications sold to merchants. However, it was retired, and the Software Security Framework replaced it, so old validation no longer helps you.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
What PCI PA DSS was
The Payment Application Data Security Standard covered commercial payment software. So merchants could choose applications that had been checked against a standard.
Why PCI PA DSS ended
PCI SSC moved to a broader framework for modern software. Therefore PA-DSS validations expired in October 2022, and the list became historical.
| Then | Now |
|---|---|
| PA-DSS validated application | Secure Software Standard validation |
| Application-only focus | Software and the vendor's development lifecycle |
PCI PA DSS transition check
Tick what you know about your payment software.
Your result appears here as you tick, so you can see what is still open.
What PCI PA DSS retirement means for merchants
An application validated under PA-DSS is not automatically insecure. However, its old validation no longer supports your PCI DSS assessment. So your QSA assesses it like any other software in scope.
Questions for software vendors
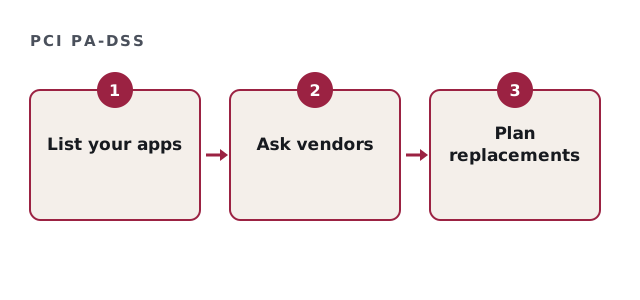
Ask what the vendor has done since. For example, whether the product holds Secure Software Standard validation.
- Is the product validated under the Secure Software Standard?
- Is the vendor's lifecycle validated under the Secure SLC Standard?
- Which version are we running, and is it supported?
- How are security updates delivered?
Where we help
We inventory payment applications and prepare the evidence your QSA will need. We are not a QSA. The current framework is described on the PCI Software Security Framework page.
Also check older terminals and back-office software. Because they were bought years ago, nobody may remember their validation status. So an inventory often reveals forgotten applications. In addition, plan replacements around your assessment calendar, because a mid-cycle change complicates evidence. As a result, the transition stays orderly rather than rushed.
PCI PA DSS questions
Is PCI PA DSS still valid?
No. PA-DSS validations expired in October 2022.
What replaced PCI PA DSS?
The PCI Software Security Framework, with its Secure Software and Secure SLC standards.
Do we have to replace PCI PA DSS software?
Not automatically. However, it must be assessed like other software in scope.
Does vendor validation make us compliant?
No. It helps, but your own PCI DSS controls still apply.
Related guides
Plan your PCI PA DSS transition
List your payment applications and we reply with a written estimate, usually inside one business day. Also include the version numbers, because support status depends on them.
Get my written estimate