Guide
TPSP PCI obligations: managing your third-party service providers
TPSP PCI rules cover the third-party service providers that touch your card data or its security. So outsourcing a function does not outsource the responsibility for it.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
What a TPSP is in PCI terms
A third-party service provider stores, processes or transmits account data for you. Also, it can affect the security of that data. For example, a hosting company or a managed firewall service.
Core TPSP PCI requirements
Requirement 12.8 sets the obligations for merchants. However, each one needs evidence.
| Obligation | Evidence |
|---|---|
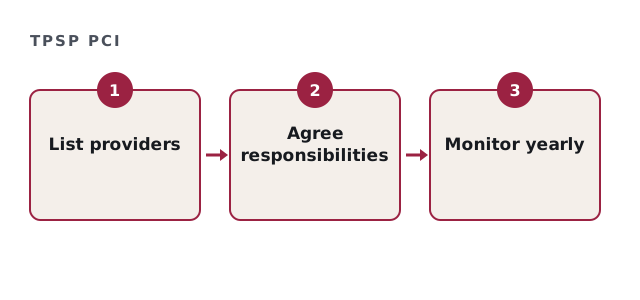
| List every TPSP | A current list with services described. |
| Written agreements | Contracts acknowledging security responsibility. |
| Due diligence | Checks before engaging a provider. |
| Annual monitoring | Proof of each provider's PCI DSS status. |
| Responsibility matrix | Which requirements each side manages. |
TPSP PCI readiness check
Tick what is in place today.
Your result appears here as you tick, so you can see what is still open.
Why the TPSP PCI responsibility matrix matters
Gaps hide between parties. For example, both sides assume the other patches a server. Therefore a clear matrix prevents controls from falling through the cracks.
Checking a provider's status
Ask for the provider's Attestation of Compliance, and check its date and scope. Also, confirm the services you use are actually covered.
Where we help
We build the provider list, the responsibility matrix and the monitoring routine. We are not a QSA. Requirement text is in the PCI SSC document library.
Also review the list whenever procurement signs a new tool. Because new services often touch card data indirectly, they can slip in unnoticed. So link the provider list to your purchasing process. In addition, keep each attestation with its expiry date, because an expired one counts as missing evidence. As a result, annual monitoring becomes a short routine rather than a scramble.
TPSP PCI questions
Is a payment gateway a TPSP for PCI?
Usually yes, because it processes account data for you.
How often do TPSP PCI checks happen?
At least annually, as part of monitoring.
What if a provider will not share TPSP PCI evidence?
Record it, consider alternatives and expect your QSA to ask about it.
Does a provider's compliance cover us?
No. It covers the provider's part only.
Related guides
Organise your TPSP PCI obligations
List your providers and we reply with a written estimate, usually inside one business day. Also mention any provider that refuses to share an attestation, because that shapes the plan. So the estimate covers the hard cases as well as the easy ones.
Get my written estimate