Guide
PCI wireless requirements, even if you do not use Wi-Fi
PCI wireless rules apply to almost every merchant, because rogue access points can appear anywhere. So even businesses without Wi-Fi must check for unauthorised wireless devices.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
Why PCI wireless rules apply to everyone
A small access point plugged into a network port can bypass every firewall. Therefore PCI DSS asks you to detect unauthorised wireless devices, whether or not you use Wi-Fi.
Core PCI wireless requirements
The rules are few. However, each needs a record.
| Requirement | Plain meaning |
|---|---|
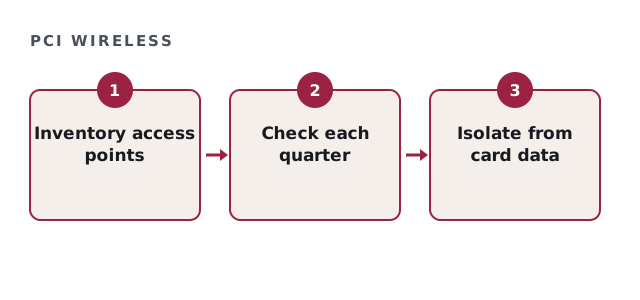
| Detection | Check for unauthorised access points at least once every three months. |
| Inventory | Keep a list of authorised wireless access points. |
| Response | Act on any unauthorised device you find. |
| Isolation | Wireless networks separated from the cardholder data environment. |
PCI wireless readiness check
Tick what is true at every location.
Your result appears here as you tick, so you can see what is still open.
Configuring authorised networks
If wireless connects to the cardholder data environment, defaults must change. For example, vendor passwords and default encryption keys. Also, strong encryption protects traffic.
Where PCI wireless evidence goes missing
Merchants often run the check but keep no record. So the QSA cannot confirm it happened.
- Scans with no date or location
- Inventories that list old devices
- No record of how a rogue device was handled
- Guest Wi-Fi sharing a network with terminals
Where we help
We set up the quarterly routine, review isolation and organise evidence. We are not a QSA. The requirement text is in the PCI SSC document library.
Also train store staff to report unknown devices. For example, an unfamiliar box near the router should prompt a question, not a shrug. So detection does not rely on the quarterly check alone. In addition, record how each finding was resolved, because the assessor will ask what happened next.
PCI wireless questions
Do PCI wireless rules apply if we have no Wi-Fi?
Yes. You still need to detect unauthorised access points.
How often are PCI wireless checks required?
At least once every three months.
Can network access control replace PCI wireless scans?
Some automated monitoring methods are acceptable, if they detect unauthorised devices reliably.
Is guest Wi-Fi in scope?
Only if it can reach the cardholder data environment, so isolate it.
Related guides
Get your PCI wireless evidence in order
Tell us how many locations you run. We reply with a written estimate, usually inside one business day. Also say whether any location uses wireless terminals, because that changes the isolation review. So the estimate covers every site.
Get my written estimate