Guide
PCI DSS PAN storage: keeping card numbers only when you must
PCI DSS PAN storage rules decide where card numbers may live and how they must be protected. So the cheapest control is usually not storing the full number at all.
- We prepare, a QSA assesses
- Published price ranges
- Written estimate, no call
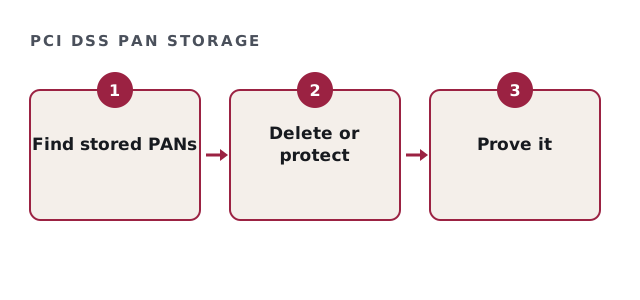
The first rule of PCI DSS PAN storage
Keep only what you need, for only as long as you need it. Therefore a written retention policy and a regular deletion process come first.
How PCI DSS PAN storage must be protected
Any stored primary account number must be unreadable. The standard allows several methods.
| Method | Plain meaning |
|---|---|
| Truncation | Part of the number is removed permanently. |
| Tokenisation | A substitute value replaces the number. |
| Keyed hashing | A one-way hash using a secret key. |
| Strong encryption | Encrypted, with keys managed properly. |
PCI DSS PAN storage check
Tick what you can prove today.
Your result appears here as you tick, so you can see what is still open.
Masking when PANs are displayed
Display is a separate rule. So screens and reports should show no more than the first six and last four digits, unless a role genuinely needs more.
Where PCI DSS PAN storage surprises merchants
Card numbers often hide in places nobody planned. For example, support tickets, call recordings, log files and exported spreadsheets.
- Customer service tickets and email
- Application and debug logs
- Backups and old databases
- Spreadsheets used for refunds
Where we help
We help you find stored numbers and reduce or protect them before assessment. Remediation runs $30,000 to $150,000 for larger estates. We are not a QSA. The standard is in the PCI SSC document library.
Also search again after each major change. For example, a new support tool can start capturing card numbers in tickets. So discovery is a routine, not a one-off project. In addition, tell staff why it matters, because a careless export can undo months of scope reduction. As a result, the cardholder data environment stays as small as you designed it.
PCI DSS PAN storage questions
Is PCI DSS PAN storage allowed at all?
Yes, if there is a business need and the number is rendered unreadable.
Does tokenisation remove PCI DSS PAN storage scope?
It can reduce scope greatly, depending on how the token system is designed.
Does PCI DSS PAN storage include backups?
Yes. Every copy counts, including backups.
Can we ever store the CVV?
No. Security codes must not be stored after authorisation.
Related guides
Reduce your PCI DSS PAN storage scope
Tell us where card data might live. We reply with a written estimate, usually inside one business day.
Get my written estimate